Cyber at the Frontier
A live keynote on the next era of cyber defense. November 12, 10:00 AM PT.
Frontier intelligence for cybersecurity
Find vulnerabilities, test defenses, and develop fixes faster with frontier models and agents.
Cyber defense needs a new playbook
AI is accelerating how attackers find and exploit vulnerabilities. Defenders can get ahead now, but their window is narrowing.
Now is the time to make defense continuous.
Put AI to work across your security program
Access cyber models through Daybreak
Daybreak provides approved access for cybersecurity work. Use Blue for defensive workflows and Red for advanced, authorized testing.

Daybreak Blue

Daybreak Red
From vulnerability discovery to verified fixes
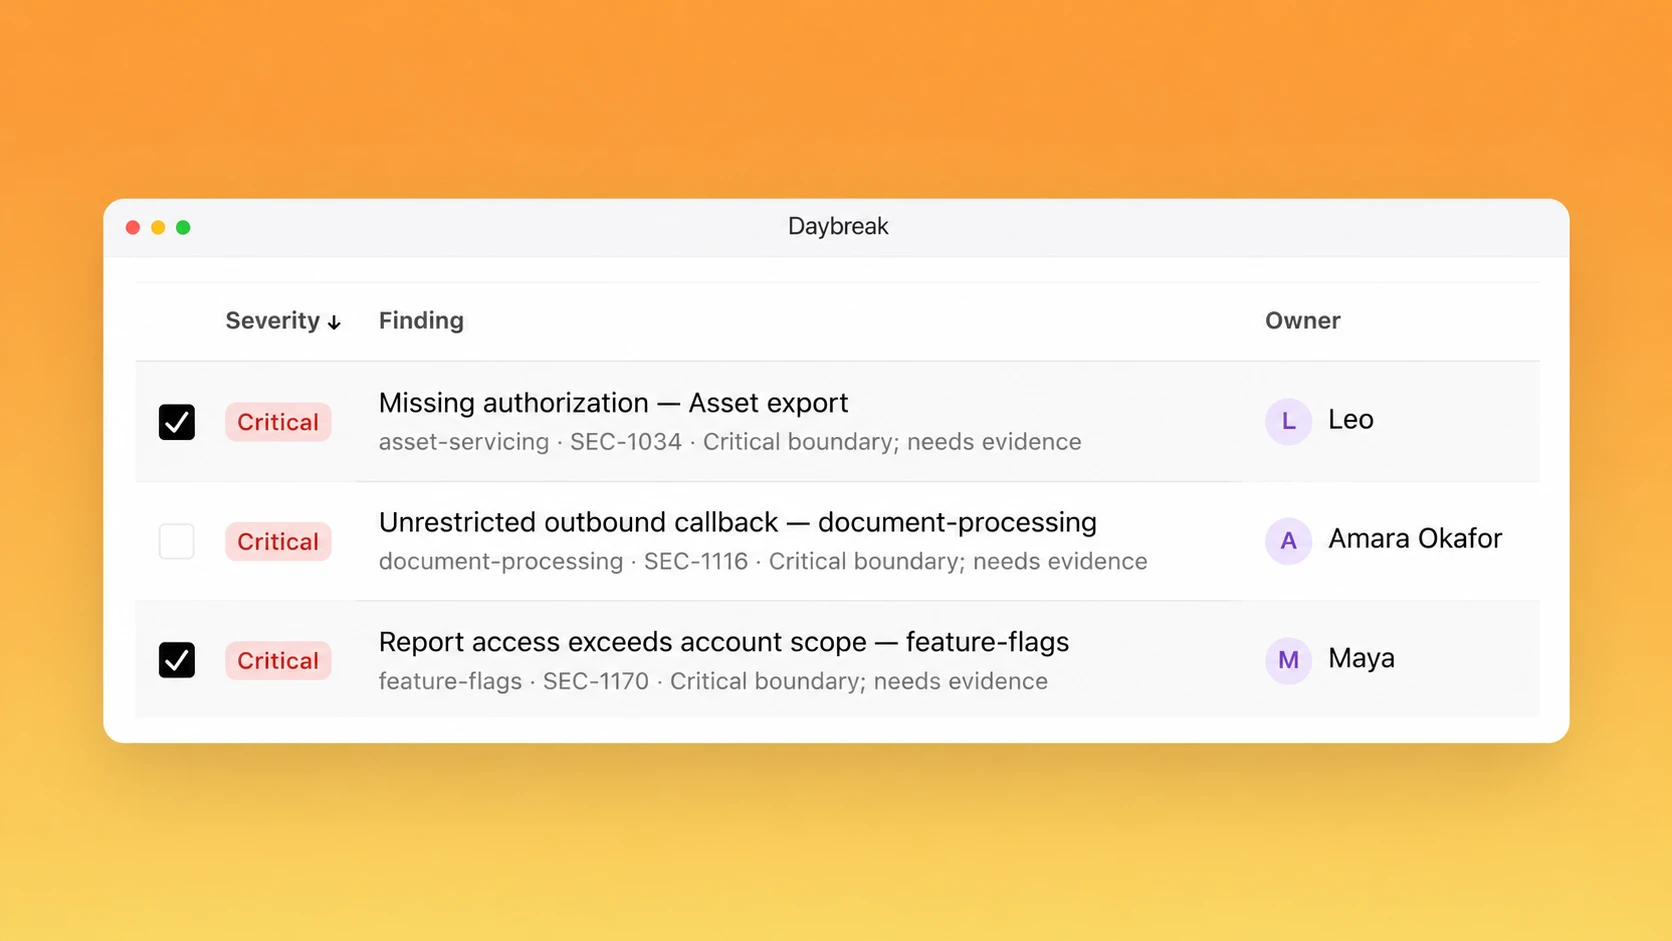
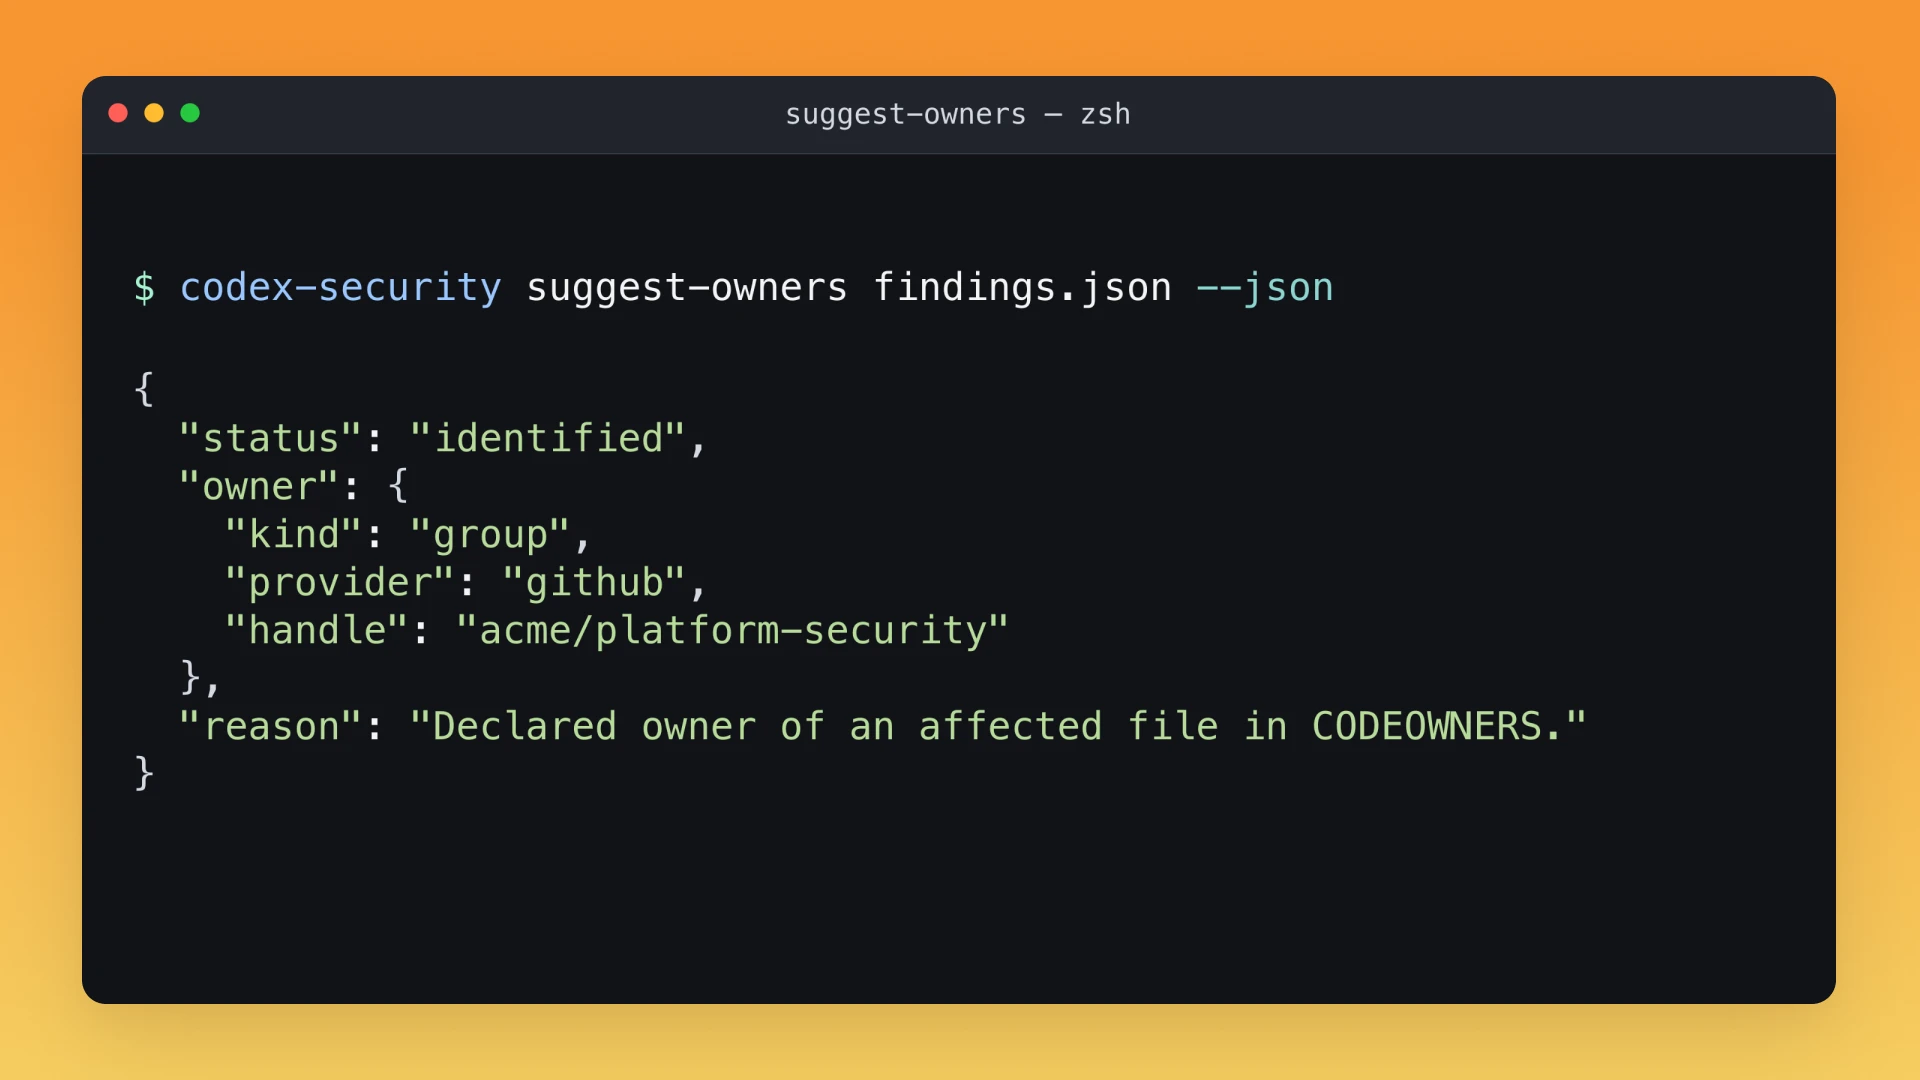
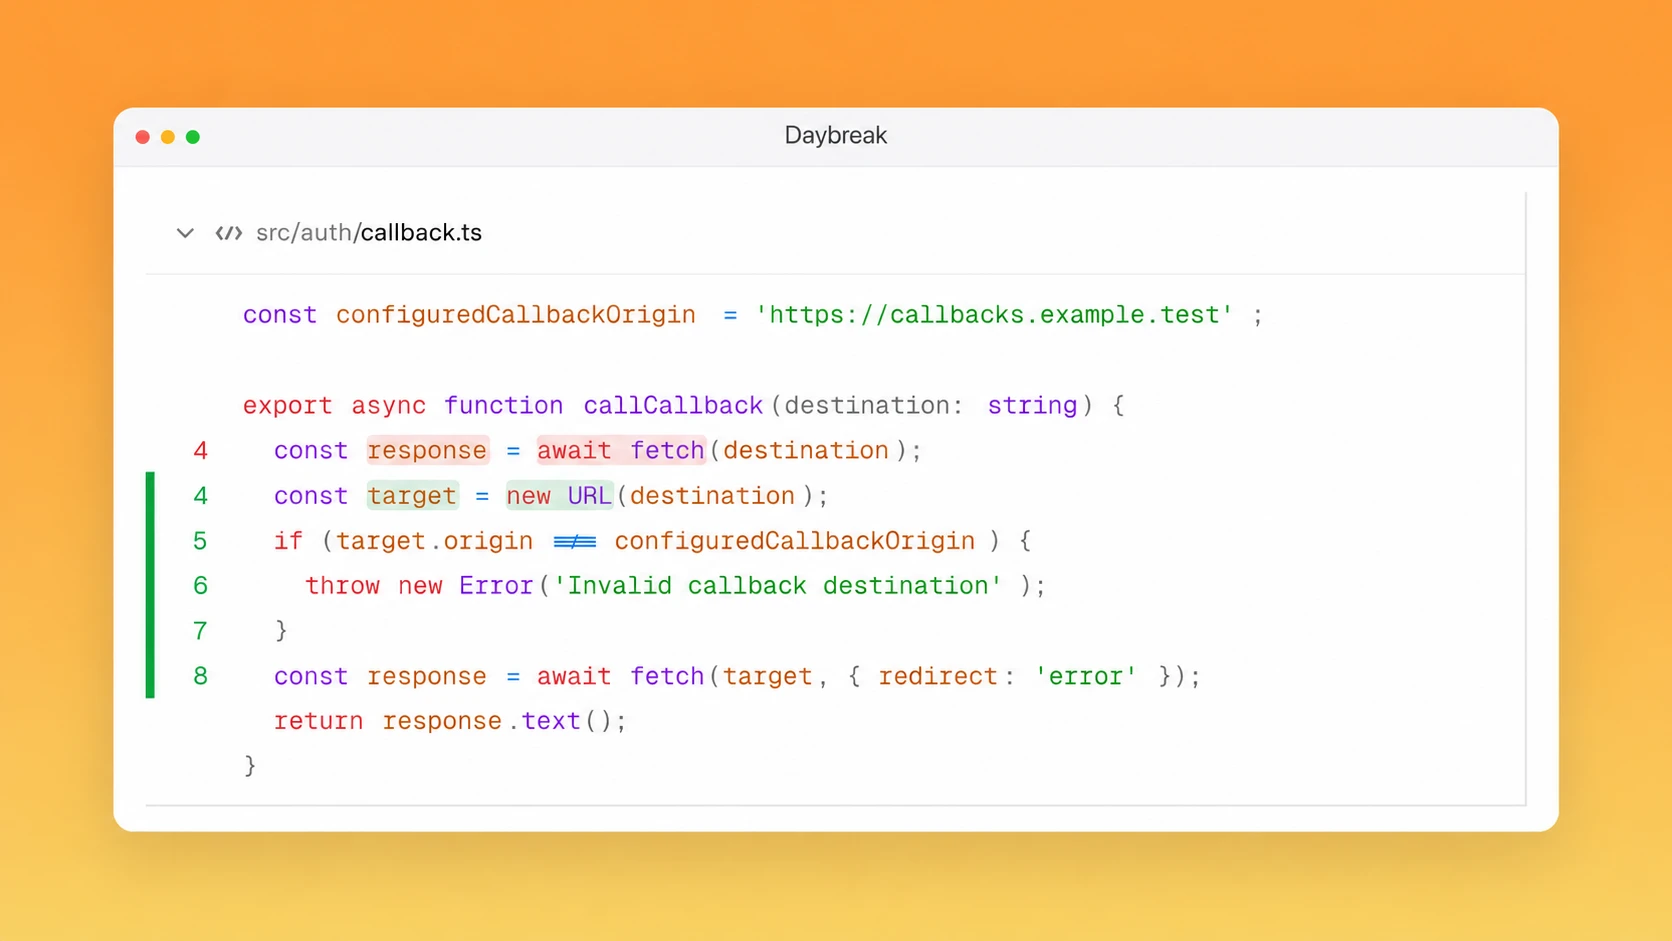
Build agentic loops to investigate findings, prioritize risk, and prepare fixes your team can review.
Secure code in the tools you already use
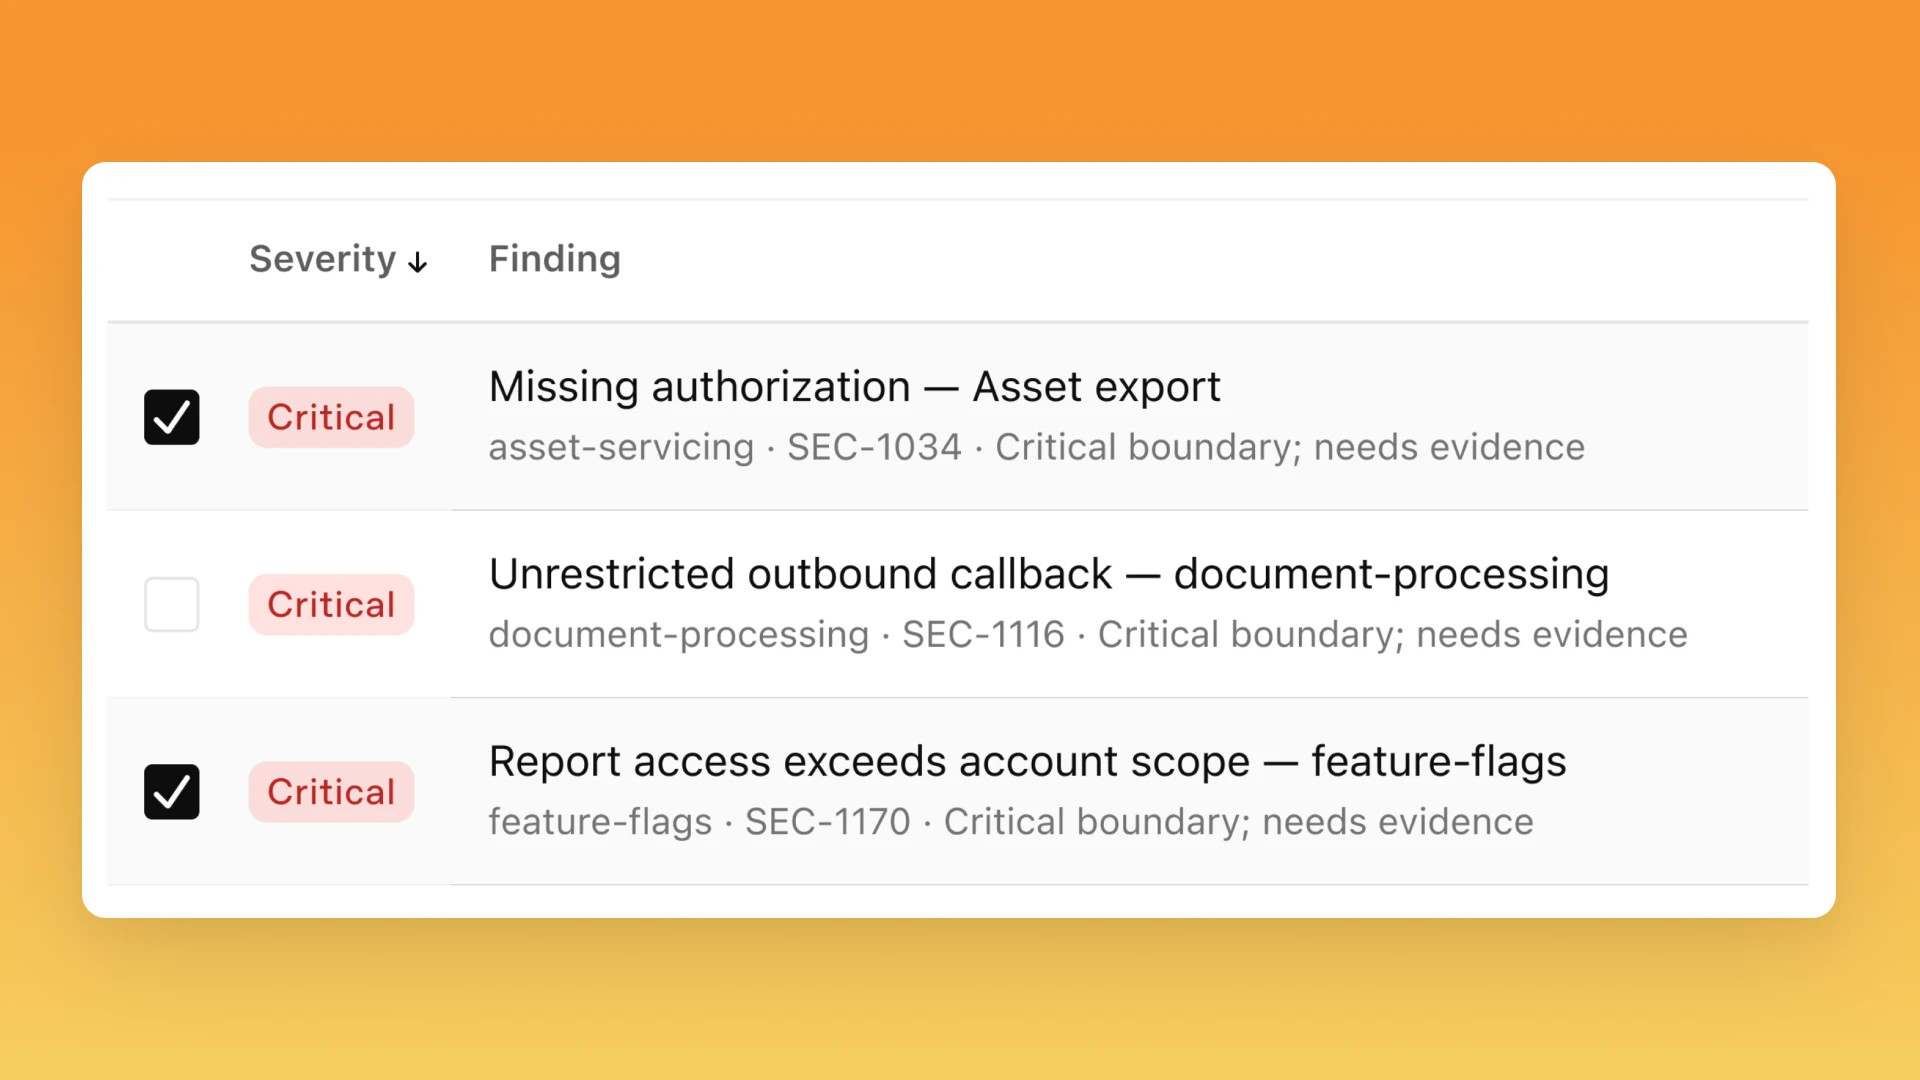
Daybreak Defense Factory
Go from findings to fixes at the push of a button. Scans and patching workflows all run remotely.
Daybreak Plugin
Scan and create patches directly in Codex, with scans running and findings stored locally.
PR review
Reduce the risk of re-introducing vulnerabilities by checking pull requests.
Building blocks for continuous defense
Codex Security CLI
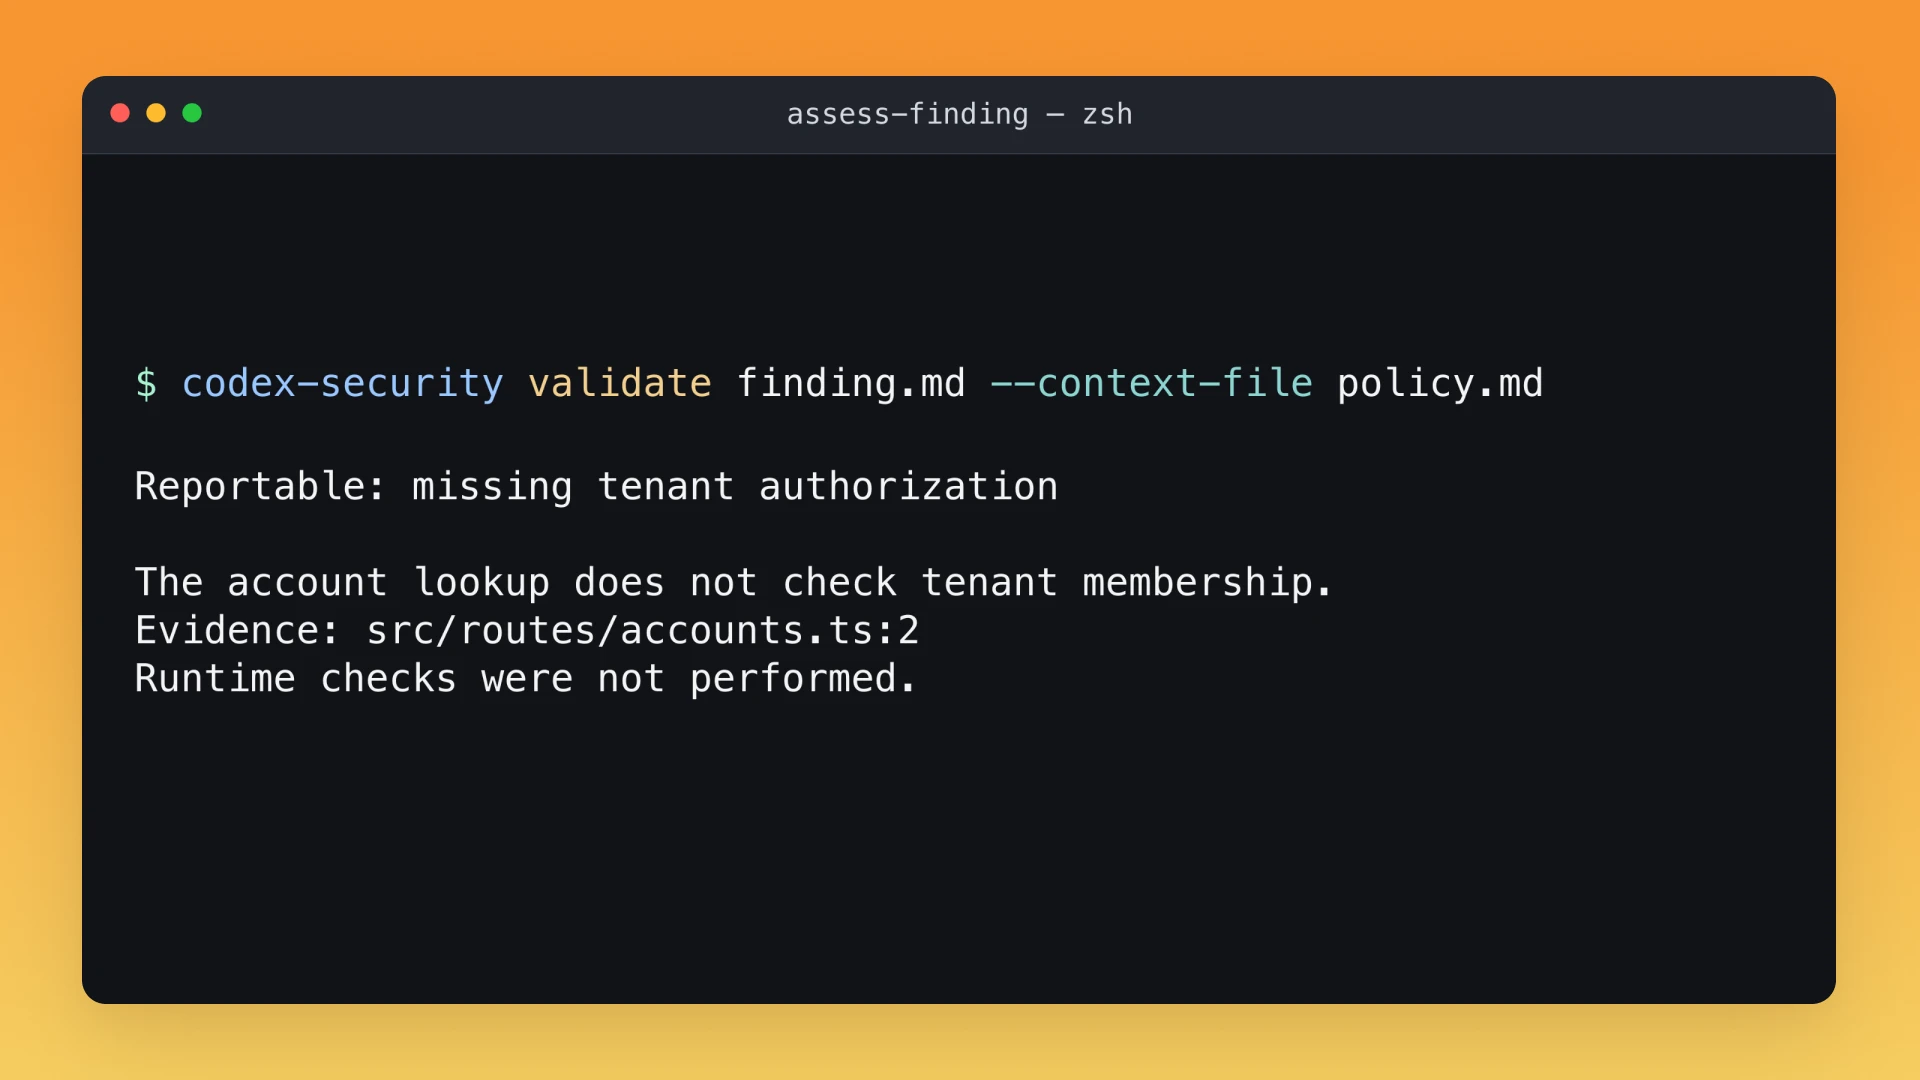
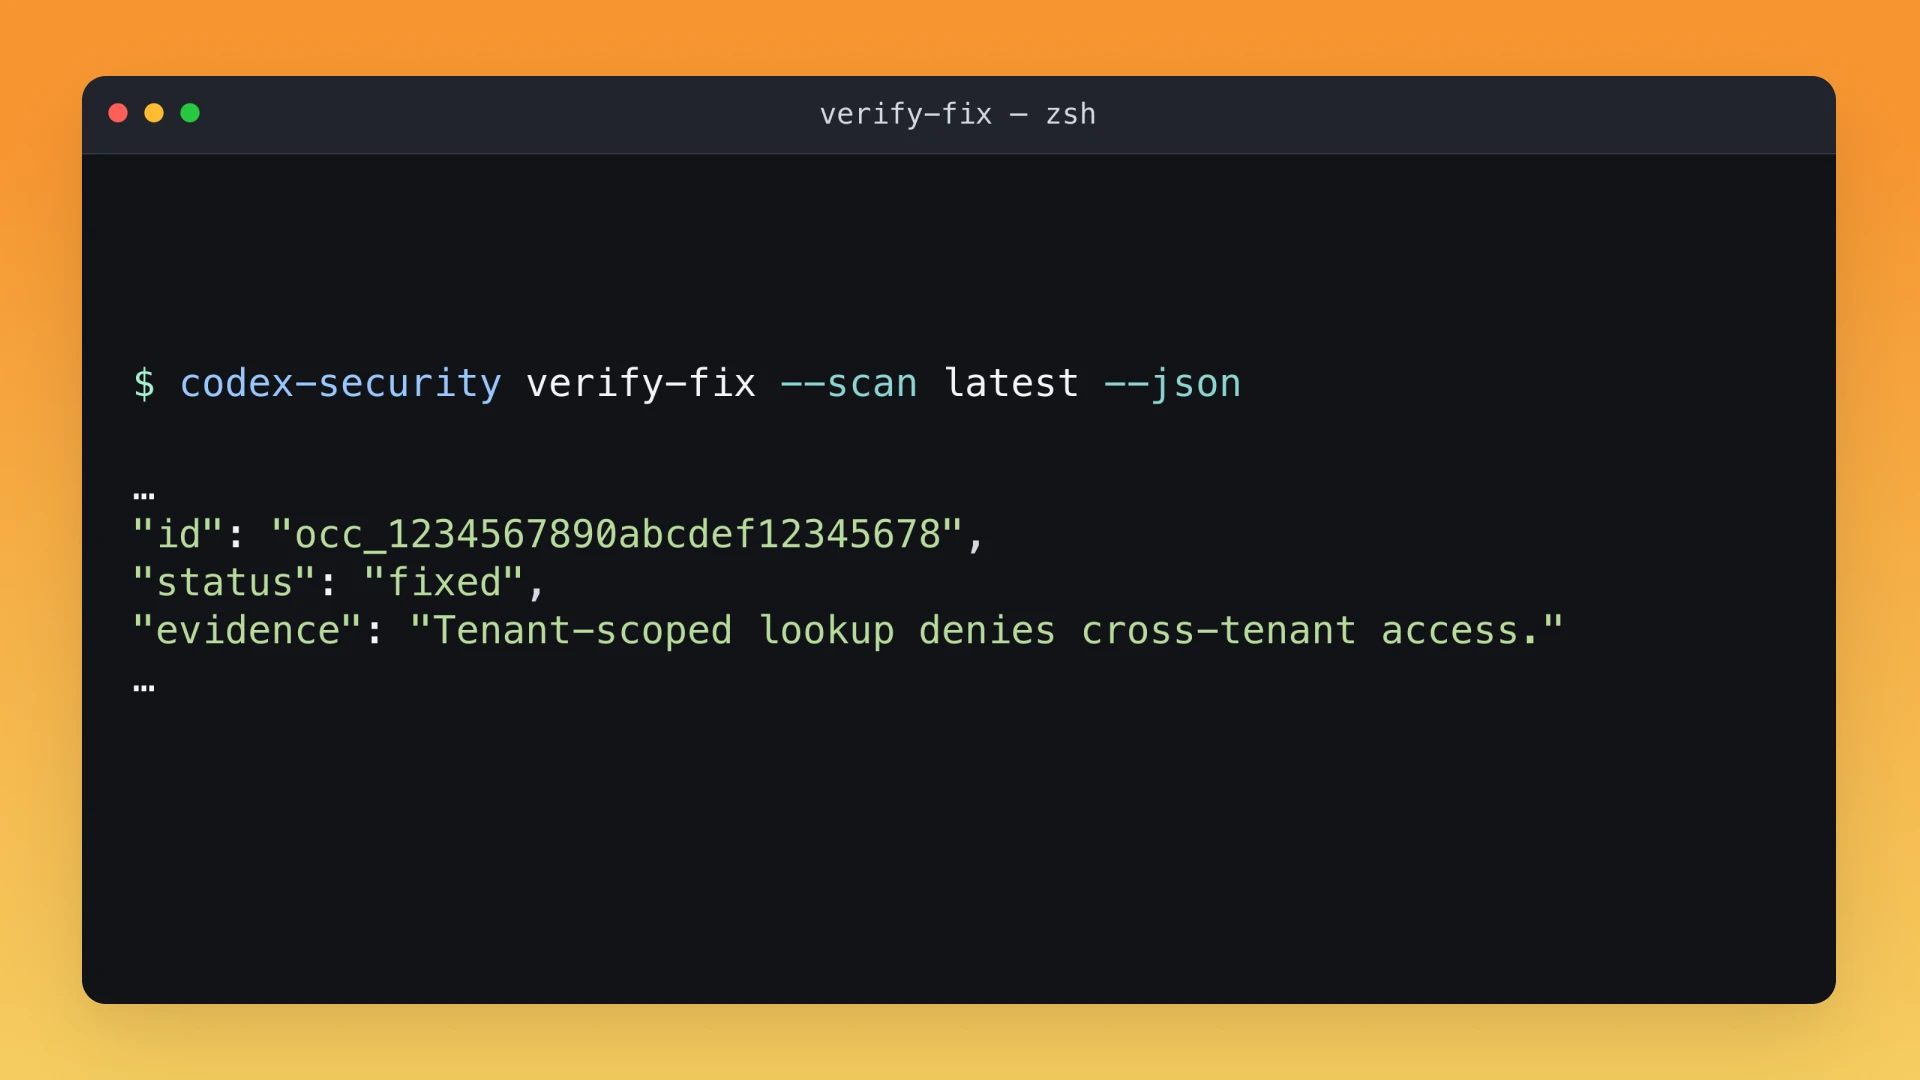
Scan code or changes from your terminal. Bring findings, coverage reports, and supporting evidence into your development workflow.
Security scans in CI
Run the Codex Security CLI in your CI pipeline alongside your existing checks.
Codex Security SDK
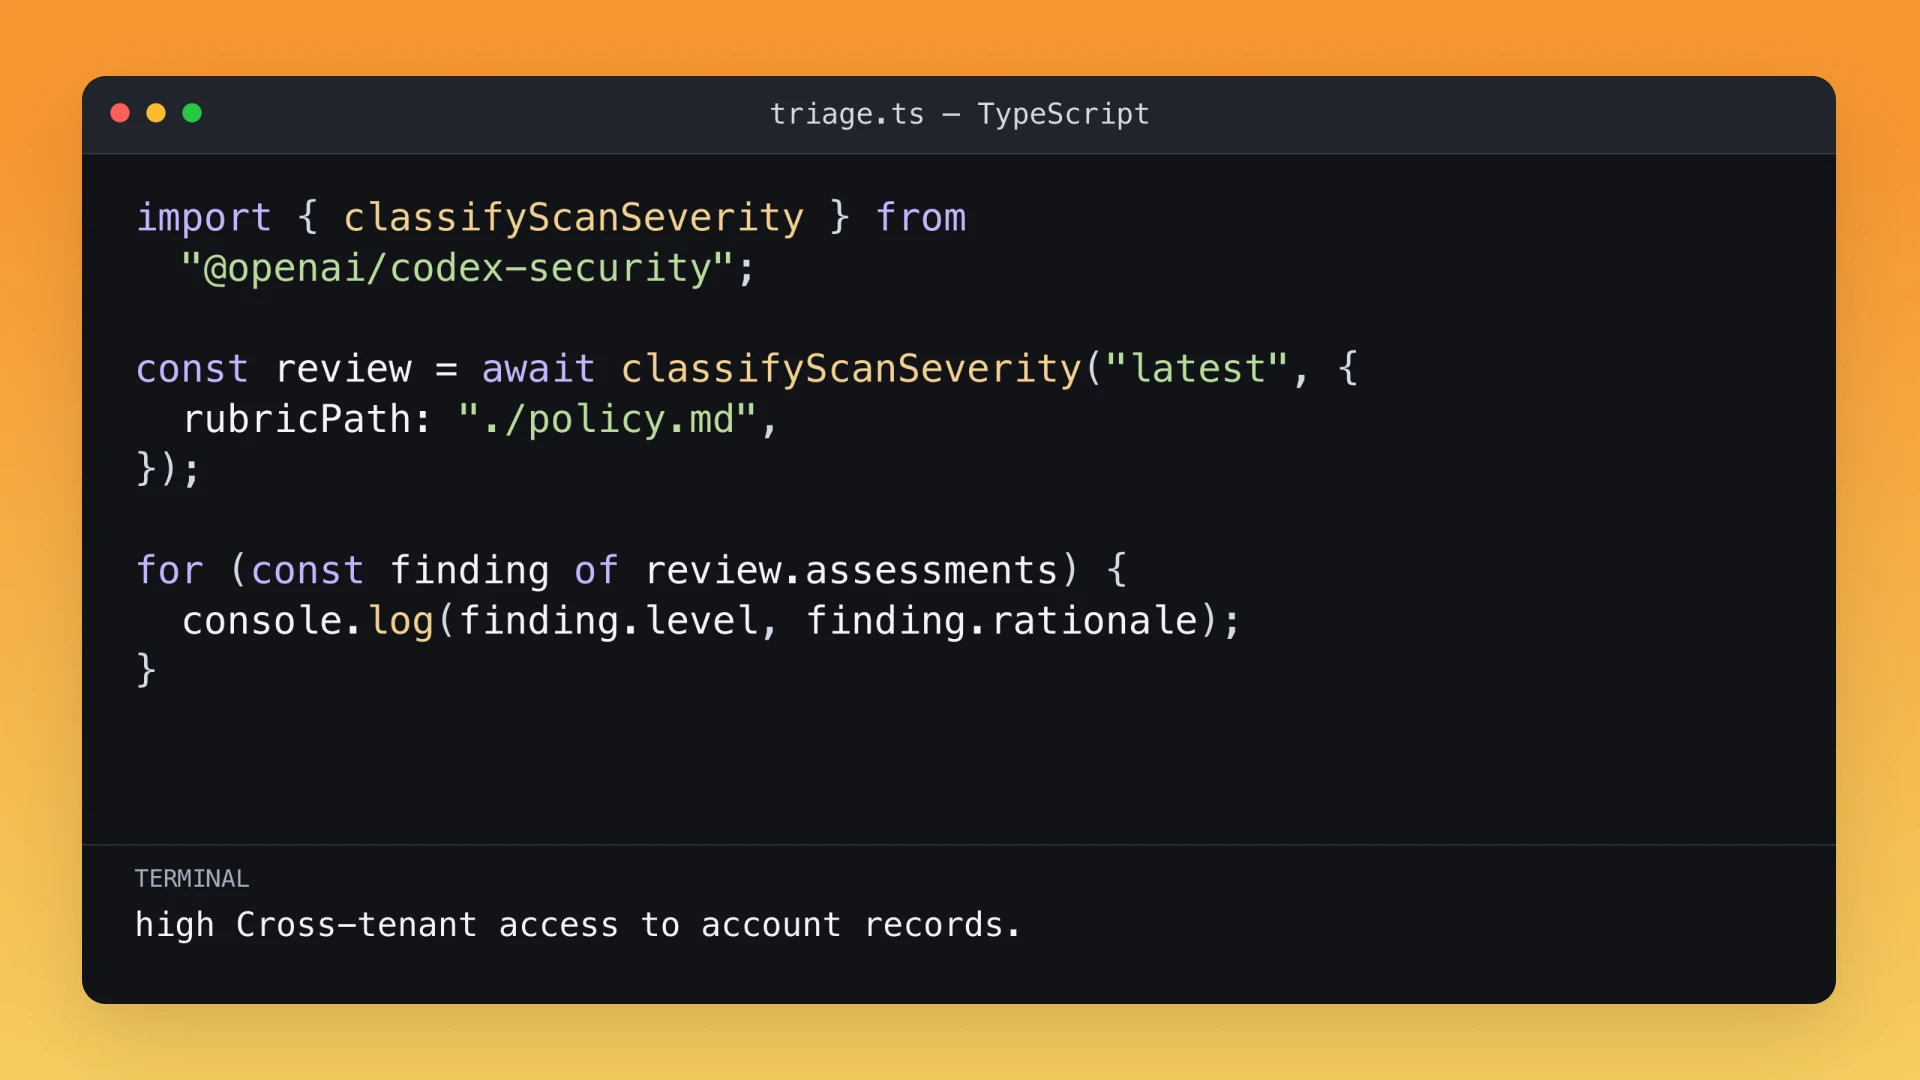
Integrate security scans into TypeScript applications, with structured findings, coverage data, and scan artifacts.
OpenAI API
Build custom security workflows using OpenAI models, along with your own tools and context.